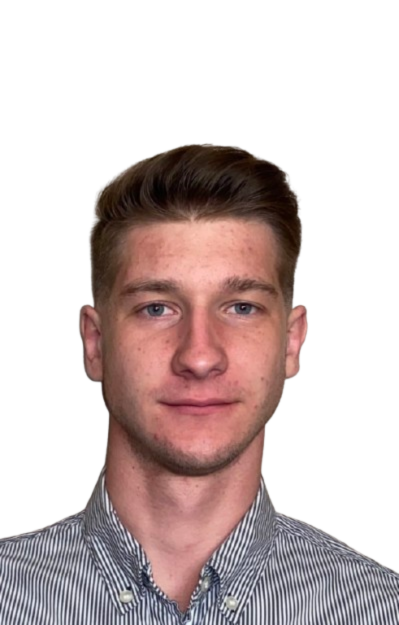
Computer Science · Information Security · 5th year · Technical University Graz
I break things to understand them — specializing in binary exploitation, mobile security, and penetration testing.
open to: junior penetration testing, mobile application security, security engineering, and security research roles
about
I'm Teodor Zlatar, a fifth-year Information Security student at Technical University Graz, expected to graduate in February 2028. My focus sits at the intersection of low-level systems and real-world attack surface — understanding not just that something is vulnerable, but precisely why and how.
I've conducted hands-on penetration tests against Active Directory forests and Linux servers, performed Android application security analysis including MITM interception and APK reverse engineering, and solved web application security challenges spanning SQL injection, path traversal, JWT attacks, and cryptographic weaknesses.
I'm continuously pushing deeper — currently focused on binary exploitation, with the longer-term goal of diving into Android and iOS internals to understand mobile platform security at a deeper level. When I'm not at a terminal, I'm on the tennis court. I find the same deliberate practice mindset applies to both.
I also care about the defensive side of security: threat modeling, secure application design, and building development processes that reduce vulnerabilities before code reaches production.
languages
skills
Exploitation & Reverse Engineering
Active Directory Testing
Linux Server Security
Web Application Security
Android Security
Digital Identity & Trust Systems
Cryptography
Programming Languages
currently
Active Practice
Working through pwn.college's binary exploitation track — heap corruption, tcache poisoning, ROP chain construction, and bypassing modern mitigations like PIE, ASLR, and stack canaries.
Planned Next
Planning a deeper dive into the Android platform from a security perspective — ART runtime internals, Binder IPC, and native library analysis to understand what actually needs protecting.
Planned Next
Intending to go beyond app-layer security into XNU kernel internals, Mach-O parsing, and sandbox architecture — understanding the platform deeply enough to reason about its defenses.
self-study
security-work
Pentesting Lab — Linux Server
Full compromise of a Linux web server from unauthenticated access to root. Found 5 vulnerabilities including SSTI, exposed .git repo, SUID misconfiguration, and Ansible sudo abuse.
Pentesting Lab — Active Directory
Full forest compromise of AD environment. 22 vulnerabilities found — including ADCS ESC8, Golden Ticket forgery, Kerberoasting, AS-REP roasting, and DLL hijacking.
Mobile Security Hacklets — reyammer.io
Solved Android security challenges across app development, reversing, and exploitation categories — including DEX class loading, native library reversing with Ghidra, PIN cracking, and calling app components that were implicitly exported through intent filters.
SEAD Web Security Challenges
Solved 9 web security challenges including JWT algorithm confusion, cookie forgery, SQL injection with WAF bypass, path traversal via Unicode normalization, file upload RCE, and TOTP brute force.
Android App Analysis — Mobile Security
Intercepted and analysed HTTPS traffic from 3 real Android apps using Burp Suite, APK patching, and static analysis. Cross-referenced findings with Google Play Data Safety claims.
Due to academic and course policies, full reports are confidential — but I'm happy to discuss methodologies, tools used, and lessons learned. Feel free to reach out if you have questions or want to talk through any of these.
projects
Alongside security-focused work, I keep several software and machine learning projects here to show broader engineering ability, data handling, and model-building fundamentals.
dino-duel
Capstone project at Harding University — a full Battle Sheep board game built in the Godot engine with local, LAN multiplayer, and AI opponents at multiple difficulty levels. I led game core development and co-led AI, implementing Monte Carlo Tree Search with parallelisation for the strongest difficulty.
ultimate-tictactoe
AI opponent for Ultimate Tic Tac Toe built as part of an Artificial Intelligence course. Uses Minimax with Alpha-Beta Pruning and time-limited recursion for real-time intelligent play across a 9×9 meta-board.
real-estate-price-prediction
Machine learning model for real estate price prediction. Built as part of an end-to-end ML course covering data cleaning, feature engineering, model training, and evaluation.
sport-person-image-classifier
Image classification model that identifies athletes from photos. Explores CNN architectures and transfer learning as part of a computer vision module.
potato-disease-classifier
Deep learning model trained to detect potato plant diseases from leaf images. Applied data augmentation and CNN training for agricultural computer vision use cases.
More on github.com/tzlatar
contact
Whether you have a question about my research, want to discuss a challenge I've worked on, need help understanding a security concept, or are interested in working together — I'm happy to hear from you.
I can't share confidential course reports, but I'm always glad to talk through methodology, tools, or findings. No question is too basic — feel free to reach out.
I typically respond within a day or two.